Siemens Product Security Advisory Policy
At Siemens, the security of our products, solutions, and services is paramount. We are dedicated to delivering reliable and secure technology, and we understand that transparency and timely communication are crucial when security vulnerabilities are discovered. This document outlines our approach to managing and communicating product security vulnerabilities through our Security Advisory Program, ensuring you have the information you need to protect your operations.
What is a Siemens Security Advisory?
A Siemens Security Advisory is a formal communication issued by the Siemens Product Security Incident Response Team (PSIRT). Its purpose is to inform our customers, partners, and the public about security vulnerabilities identified in Siemens products, solutions, or services. These advisories provide essential information to help you understand the risk and take appropriate action.
What You Can Expect from Our Advisories
When a security vulnerability is identified and confirmed in a Siemens product, you can expect our advisories to provide:
- Clear Identification: Each advisory has a unique identifier (e.g., SSA-XXXXXX), each vulnerability has a unique identifier (e.g., CVE-XXXX-YYYYY) and clear publication/update dates.
- Affected Products and Versions: A detailed list of all Siemens products and specific versions that are impacted by the vulnerability.
- Vulnerability Description: A concise and understandable explanation of the security vulnerability, including its nature and potential impact.
- Severity Assessment: Utilization of the industry-standard Common Vulnerability Scoring System (CVSS) to provide a numerical score and vector string, allowing you to quickly gauge the severity and potential risk.
- CVE Identifiers: Inclusion of Common Vulnerabilities and Exposures (CVE) identifiers, which are standard names for publicly known security vulnerabilities.
- Mitigation and Remediation Guidance: Crucially, each advisory will provide actionable steps you can take. This includes:
- Patches or Updates: Information on available software updates, firmware, or patches to resolve the vulnerability.
- Workarounds: If a permanent fix is not immediately available, we will provide recommended temporary measures to reduce the residual risk.
- Configuration Changes: Instructions for adjusting product settings to mitigate the vulnerability.
- Acknowledgements: We believe in recognizing the contributions and efforts of security researchers and organizations who responsibly disclose vulnerabilities to us.
- Contact Information: Clear guidance on how to reach the Siemens PSIRT for further assistance or to report new vulnerabilities.
These data points are available in human readable HTML and machine readable CSAF formats, which is distributed via the ROLIE feed. Details can be found in https://www.siemens.com/.well-known/security.txt, as required by the CSAF standard and RFC 9116.
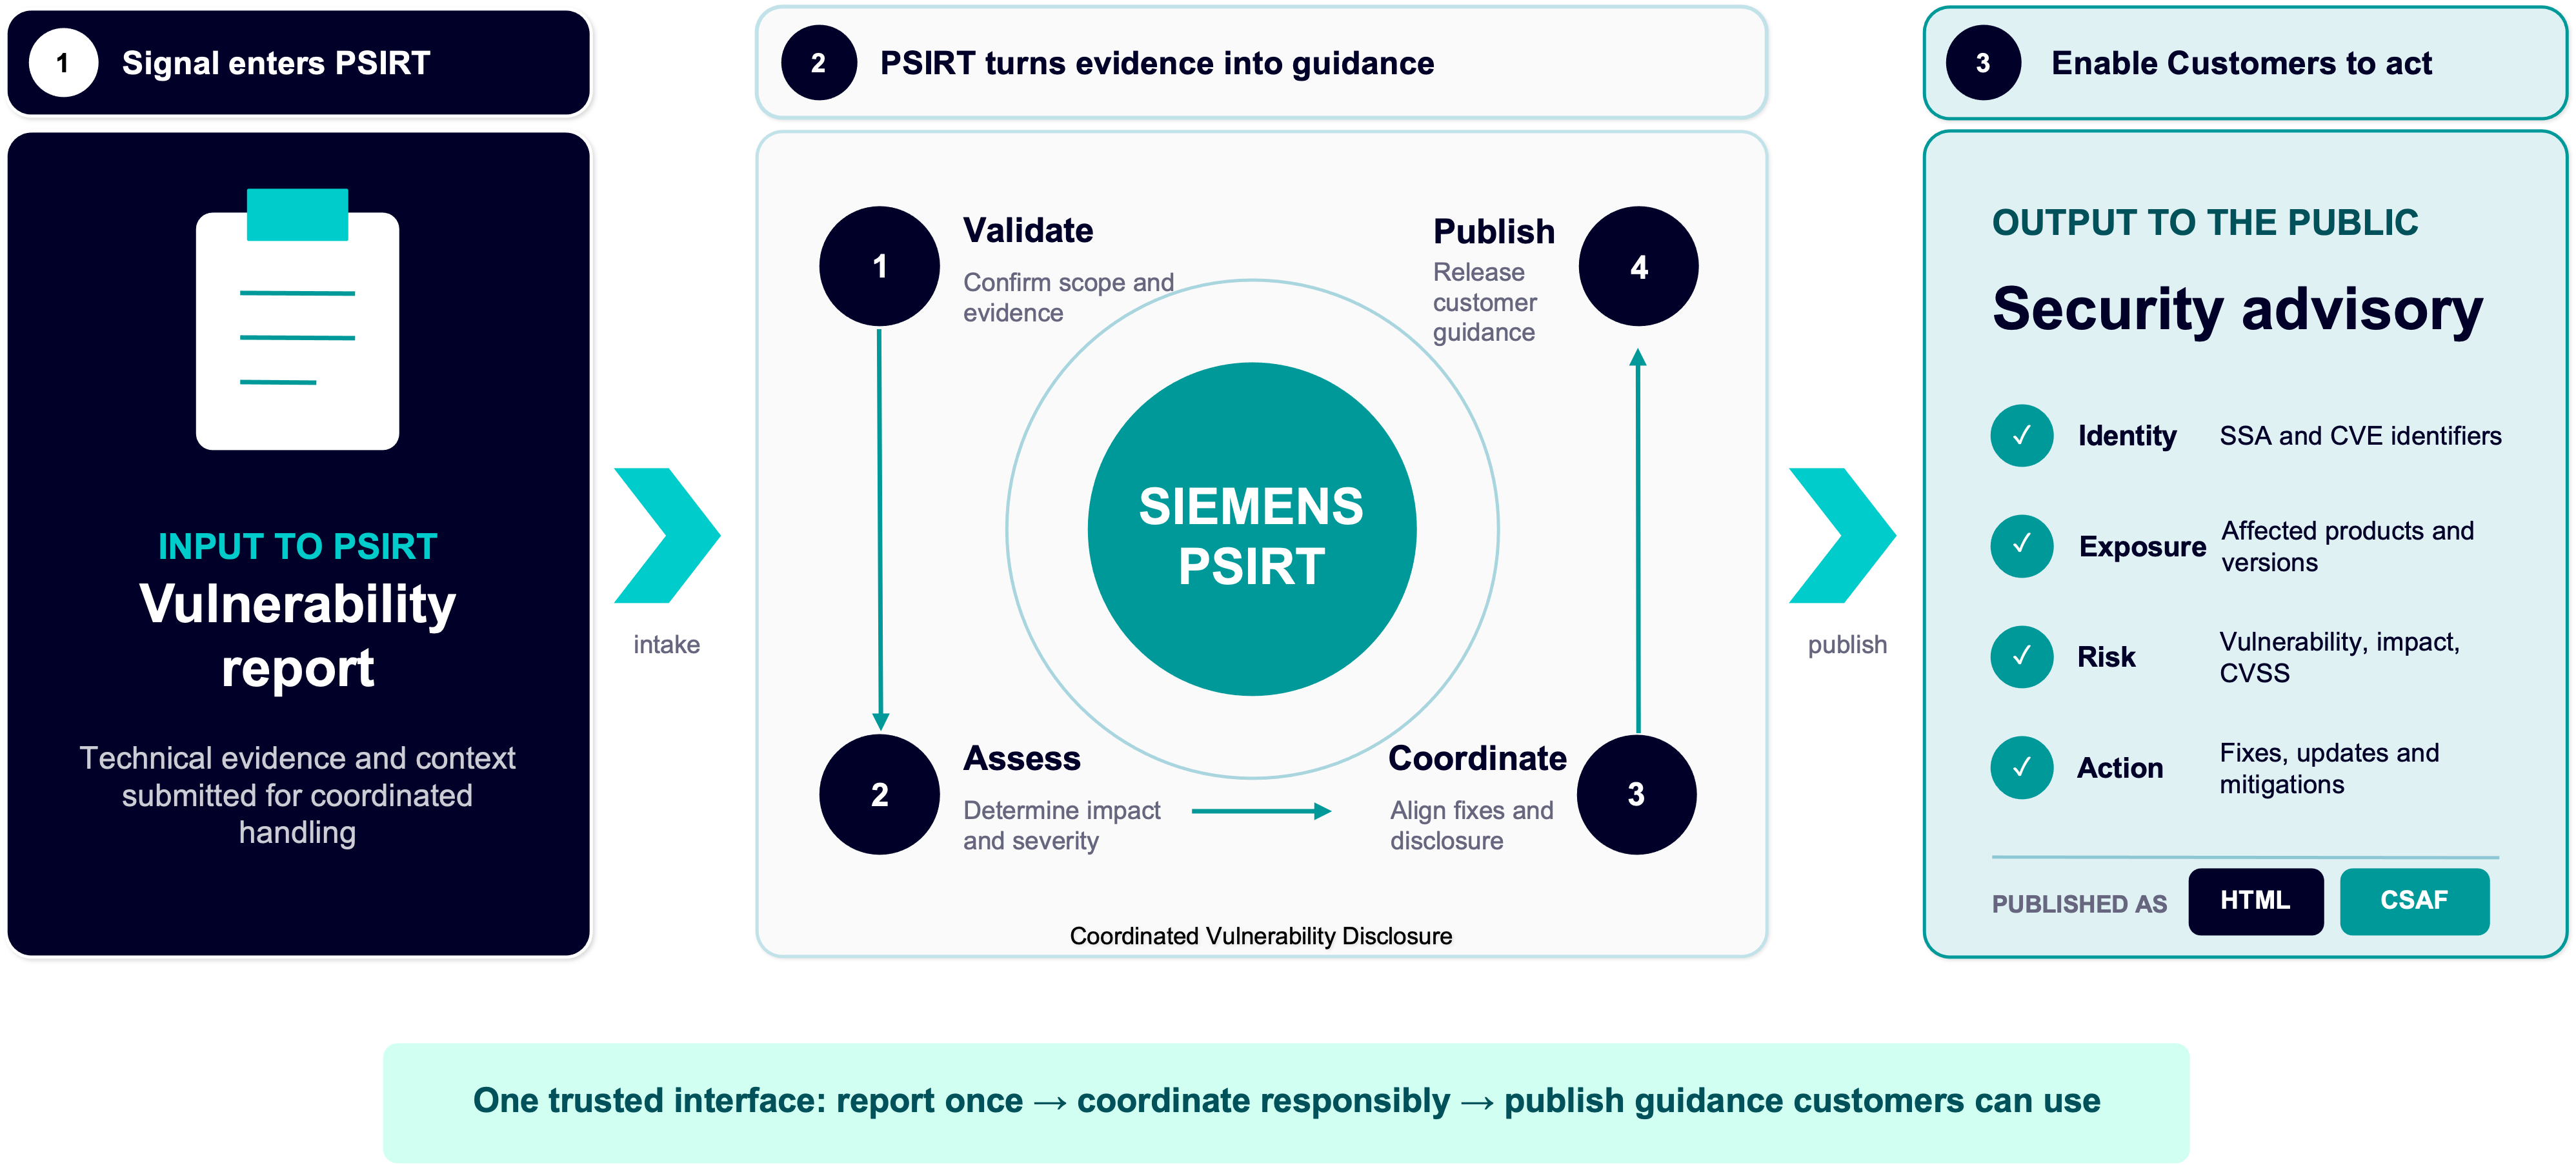 Figure 1. PSIRT Interfaces: end-to-end Siemens PSIRT coordinated vulnerability disclosure process.
Our Process: Ensuring Timely and Accurate Information
Our dedicated Product Security Incident Response Team (PSIRT) follows a structured and rigorous process to manage security vulnerabilities, from discovery to resolution and communication. This process is designed to ensure:
- Prompt Action: We prioritize the rapid assessment and containment of vulnerabilities to minimize potential impact.
- Thorough Analysis: Our experts conduct in-depth technical analysis to understand the root cause, impact, and exploitability of each vulnerability.
- Coordinated Disclosure: We strive for responsible disclosure, often coordinating with external researchers and other affected parties before public release. If multiple products are affected by the same vulnerability, our goal is to publish all affected products at the same time to inform all affected customers.
- Effective Solutions: We work closely with our product development teams to provide robust and timely fixes. In case fixes are not or not yet available for some products, we publish specific mitigations.
- Consistent Communication: All advisories adhere to a standardized format and content guidelines to ensure clarity and ease of understanding.
Where to Find Our Security Advisories
All official Siemens Product Security Advisories are published on our dedicated PSIRT website: https://productcert.siemens.com/
We encourage you to regularly visit this site and subscribe to our security notification service (if available) to receive timely updates directly.
Reporting a Potential Vulnerability
Siemens encourages responsible disclosure of security vulnerabilities. If you believe you have found a security vulnerability in a Siemens product, solution, or service, please report to mailto:productcert@siemens.com (Encryption: https://productcert.siemens.com/productcert/pgp/productcert-siemens-com.asc)
Your cooperation helps us maintain the security and integrity of our offerings.
Continuous Improvement
We are committed to continuously improving our product security posture and our advisory program. We regularly review and refine our processes and communications based on a variety of critical inputs, including:
- Laws and Legal Obligations: Ensuring compliance with all relevant regulations.
- Standards and Industry Best Practices: Adhering to recognized security standards and evolving industry guidelines.
- Lessons Learned: Incorporating insights from past incidents and improvements within the broader security community.
- Customer Feedback: Valuing and integrating requests and suggestions from our customers.
- Internal and External Stakeholder Input: Considering all relevant feedback to enhance our program.
We also recognize the importance of providing reliable and consistent information across diverse industrial domains and over many years. Therefore, all change requests to our processes and advisory content undergo thorough evaluation by all stakeholders, followed by careful implementation and testing, to maintain the highest level of accuracy and trustworthiness.
Enhancements Currently in Our Pipeline:
We are actively working on several key improvements to our Security Advisory Program to further enhance your experience and access to information:
- API for Querying Products and Vulnerabilities: Developing an Application Programming Interface (API) to allow automated querying of our product and vulnerability data.
- Increased Coverage of Third-Party Vulnerabilities: Expanding our efforts to include more comprehensive information on vulnerabilities originating from third-party components within our products.
- Increased Coverage of "Not Affected" Products: Providing clearer and more extensive statements on products that have been confirmed not to be affected by specific vulnerabilities.
- Increased Integration into Third-Party Vulnerability Databases: Working towards better integration of our advisory data into widely used external vulnerability databases.
Items Currently Not in Our Pipeline:
While we are always evaluating new features, the following items are not currently planned for inclusion in our Security Advisory Program:
- SSVC Ratings: Adoption of Stakeholder-Specific Vulnerability Categorization (SSVC) ratings.
- Improvements in Product Descriptions: Enhancements to the general product descriptions within advisories beyond security-specific details.
- Non-Vulnerability Related Information: Inclusion of information not directly related to security vulnerabilities (e.g., region-specific or industry-specific operational details).
Version History
| Version | Changes | Date (dd/mm/yyyy) |
|---|---|---|
| 1.0 | Initial Publication | 12/11/2026 |